CMS Wallet Security: A Boundary-by-Boundary Checklist
Review secrets, scripts, permissions, protected content, payment recovery, and incident controls before release.
Read the guideA connected reading path through 6 CMS Wallet Lab articles.
Review permissions and data handling across the publication, browser, and trusted services. This collection approaches security through concrete decisions: what a request proves, which component may grant access, where protected material lives, and what support may inspect.
Use the checklist to turn concerns into repeatable release tests. The related architecture and content-model articles help assign controls to the correct component instead of relying on a prominent warning or a hidden page section.
Review secrets, scripts, permissions, protected content, payment recovery, and incident controls before release.
Read the guideModel public content, protected resources, and reviewed policy references without putting secrets in the CMS.
Read the guideBuild a token-gated content plan around verified identity, explicit access rules, and protected resource delivery.
Read the guideEvaluate wallet plugins through permissions, account linking, payment behavior, compatibility, and an exit plan.
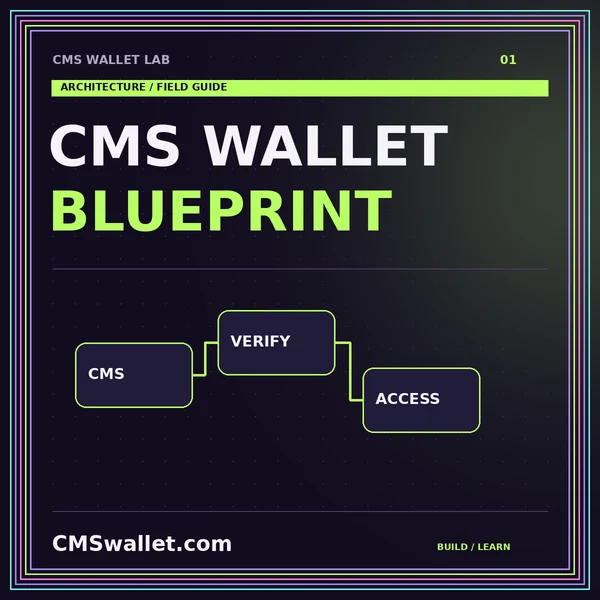
Read the guideSeparate wallet connection, identity, permissions, and payments before building a CMS wallet integration.
Read the guideDesign an Ethereum sign-in workflow with clear consent, challenge verification, account changes, and session boundaries.
Read the guide